 Switch to seedless. 30% off with SWITCH30 until 02 Nov


Ledger Cryptobilis Incident: How Complexity Creates Security Risks
The simpler the wallet, the more difficult it is to fit anything extra inside.
This article is available in the following languages:
Key facts
Ledger is investigating reports of reportedly $100 million in fund losses linked to devices sold through CryptoBilis.
They confirmed that one impacted user's wallet contained an unauthorized hardware implant that captured seed phrases.
The lesson:
A stolen seed phrase can give attackers control of a wallet.
More hardware components create more potential attack vectors
Supply chain is a new risk factor, not just the secure element.
How Tangem’s design addresses these risks:
Seedless by design. No seed phrase. Nothing to steal that way.
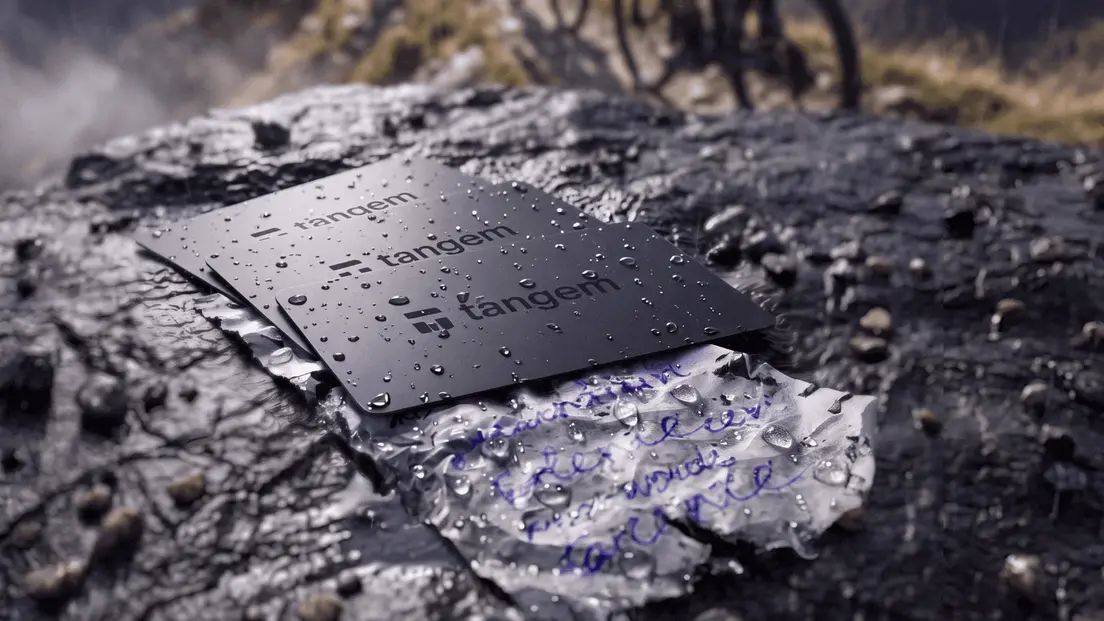
Just a card. No screen, battery, USB, or Bluetooth. Fewer components, fewer attack vectors.
Buy anywhere. Verify in the app. The Tangem app verifies your wallet’s authenticity and warns you if it was activated before you received it—even if it came from a compromised reseller.
What's the Ledger Cryptobilis incident about?
On October 9, 2026, Ledger said it is investigating reports of loss of funds from users in Southeast Asia who bought through CryptoBilis, a reseller, and asked it to pause sales. Onchain estimates put the losses above $86 million. Ledger identified the cause as unauthorized hardware implants embedded in one user's wallet.
The discussion around this incident highlights a fundamental principle of hardware security: the more complex a device is, the more potential attack vectors it introduces. Screens, batteries, communication modules, internal wiring, and additional chips may improve functionality, but they also create more opportunities for attackers to interfere.
Whatever the mechanism, onchain analysis by Bitquery indicates one actor held the victims’ keys. Seed phrases remain one of crypto's biggest security risks. Whether exposed through phishing, social engineering, physical tampering, or compromised devices, a stolen seed phrase can give attackers complete remote control over a user's funds. The cryptography doesn't need to be broken if the recovery phrase itself is compromised.
What could have happened?
In August 2025, someone on Reddit posted photos of a Ledger Nano X they had bought secondhand in Thailand. The battery was too small, and a second hand-wired board with its own antenna sat glued next to the legitimate circuit board. According to hardware security researcher Joe Grand's analysis, the wallet powered on fine and passed Ledger's built-in authenticity check.
Grand spent months pulling the Ledger device apart: decapsulating the implant's microcontroller, extracting the firmware, and analyzing the radio signals. He published the full teardown at hardwear.io USA 2026 and released the extracted firmware.
Fast forward to October 9, 2026. Users across Malaysia, Indonesia, and the Philippines are starting to post on X and Reddit: wallets drained, funds gone. Ledger said the reports came from users who bought through CryptoBilis. Blockchain analytics firm Bitquery later put the figure at $92.9 million across 311 wallets on five blockchains.
How the implant Joe Grand analyzed worked
While the investigation is still ongoing, this section describes the single device Joe Grand examined.
The Ledger Nano X keeps private keys inside a certified secure element. On paper, that makes it safe, but the chip has to talk to the screen. When you initialize the wallet, the device displays your 24 recovery words, which travel from the secure element to the OLED display over an SPI bus. More importantly, the data on those wires from the secure element to the display is unencrypted pixel information. This is where the implant eavesdrops to intercept information.
Joe Grand's teardown found a board marked V05 glued inside the case shell. Thin enameled copper wires ran from it to the Nano X's SPI test points. On that board: an ARM microcontroller running custom firmware decoded the pixel data in real time, recognized the BIP-39 word list character by character, and stored the full 24-word phrase.
The implant had its own communications stack: a modem, an eSIM loaded with a data-only profile, and a hand-wound coil antenna. Once it captured the seed phrase, it sent it over the cellular network to a remote server.
Why it matters: complexity creates more attack vectors
The lesson goes beyond Ledger. It raises a fundamental question about hardware wallet security: How many potential attack surfaces does a device really need?
First, complexity creates more attack vectors. Screens, batteries, communication modules, internal wiring, and additional chips may improve functionality, but they also create more opportunities for attackers to interfere. Every additional component expands the potential attack surface.
Second, seed phrases remain one of crypto's biggest security risks. Whether exposed through phishing, social engineering, physical tampering, or compromised devices, a stolen seed phrase can give attackers complete control over a user's funds. The cryptography doesn't need to be broken if the recovery phrase itself is compromised. The best way to reduce security risks is to eliminate unnecessary attack vectors.
How Tangem mitigates supply chain risks
A Tangem card has no "outside" or unnecessary components: displays, internal wiring, battery, and USB ports. The secure element and NFC antenna are sealed into a single monolithic card. There is no room for an implant and no power source to run one. The card draws power from your phone only during the few seconds it takes to sign transactions.
In a seedless setup, private keys are generated inside the secure element and never leave it. The only data sent over the NFC link is an unsigned transaction and the signature returned in response. Both are public on the blockchain, so there’s no secret in transit to intercept.
Tangem's authenticity check covers what matters
Every time you tap the card, the Tangem app challenges the chip with a cryptographic test. Only cards produced by Tangem and running authentic firmware pass this test.
Firmware injection is a known supply chain risk. Tangem eliminates the vector entirely. The firmware is burned into the chip at the factory, and the chip accepts no updates thereafter. No update channel means no injection channel.
If someone intercepts the card and preactivates it with a seed phrase and access code, the app catches it. During setup, it tells you the card was already activated. Reset it, and the chip wipes everything and generates new keys that only you control.
Whether you buy your Tangem Wallet from an official reseller, an airport kiosk, a street market, or CryptoBilis, it doesn't weaken its security. The authenticity check covers the chip, which is practically the entire wallet.
Thinking about switching to a Tangem hardware wallet? You can set it up without a seed phrase and use extra cards as convenient backups.
How to protect your crypto
Understand what the genuineness check actually checks. Ledger's software verification confirms that the secure element and firmware are authentic. It does not scan the circuit board for extra hardware because software alone cannot catch a physical implant.
Think about architecture, not just brand popularity. The implant Joe Grand analyzed exploited the wiring between the secure element and the screen. Fewer internal components mean fewer buses to tap, gaps to exploit, and less physical space to hide something.
Inspect the device before you use it. Check the packaging for signs of resealing, unusual adhesive, or misaligned labels. Compare the device's weight and dimensions with the manufacturer's published specifications. If the device feels lighter or heavier than expected, do not initialize it. The implant Joe Grand analyzed required a smaller battery, which changed the weight distribution.
The strongest security feature isn't always the one you add; it's often the attack vector you eliminate by design.
References
- Joe Grand: Reverse Engineering a Ledger Nano X Hardware Implant (hardwear.io USA 2026)
- The Ledger CryptoBilis hack took $92.9M from 311 wallets.
- Ledger Support on X: statement on CryptoBilis investigation (October 9, 2026)
- CoinDesk: Ledger investigates potential wallet tampering after reports of $86 million in crypto stolen
- Decrypt: Ledger Probes Potential Theft of $87M in User Funds Tied to Crypto Wallet Reseller
- The Block: Ledger investigates wallet drains involving CryptoBilis buyers; estimate tops $86 million in losses
- NVD: CVE-2019-14354
CryptoBilis implant FAQ
-
In October 2026 Ledger began investigating losses from users in Southeast Asia who bought devices through the reseller CryptoBilis; on-chain analysis by Bitquery put the figure near $92.9 million across 311 wallets. The cause was an unauthorized hardware implant inside a wallet that captured the user's seed phrase.
-
As analyzed by researcher Joe Grand, a small board glued inside a Ledger Nano X tapped the unencrypted SPI wires carrying recovery words from the secure element to the screen. A microcontroller decoded the pixel data, recognized the 24-word phrase, and transmitted it over a cellular modem with an eSIM to a remote server.
-
Complexity creates attack vectors. Screens, batteries, communication modules, internal wiring, and extra chips add functionality but also give attackers more to interfere with. And a stolen seed phrase hands over a wallet without the cryptography ever being broken - the recovery phrase remains one of crypto's biggest risks.
-
A Tangem card has no screen, battery, USB, or internal wiring - just a secure element and NFC antenna sealed into a monolithic card, leaving no room for an implant and no power to run one. It is seedless by default, so there's no phrase to intercept, and only public data (an unsigned transaction and its signature) crosses the NFC link.
-
The authenticity check covers what matters. Every tap, the app cryptographically challenges the chip so only genuine Tangem cards with authentic, factory-burned firmware pass - and if a card was preactivated by a compromised reseller, setup flags it so you can reset it and generate new keys only you control.
Don't miss these

